IT Operations in the Age of AI: Shadow AI, Access Permissions, and Accountability.
AI has long been part of everyday work. Employees are using new tools, sharing data, and enabling integrations—often before IT even knows about it. Meanwhile, the technology itself is evolving: AI no longer just makes suggestions. AI agents are now capable of performing tasks on their own.
In this webinar, we’ll show you how companies can regain transparency and control. Which AI tools have access to their systems? What data do they see? What permissions do they have? And how can you ensure that automated operations are traceable, restricted, and reversible if necessary?


AI tools are spreading faster than traditional IT processes can keep up with. Someone opens a new tool in their browser, links a Microsoft account, approves an integration—and within minutes, external applications have access to corporate data.
By 2029, 70% of companies may be using agent-based AI to operate their IT infrastructure.
In 2025, this percentage was still below 5%.
Source: Gartner, "Predicts 2026: AI Agents Will Transform IT Infrastructure and Operations," December 4, 2025.
By 2028, 40% of I&O organizations that deploy agent-based AI at scale in production environments may face business-critical service outages.
In 2026, this ratio is still below 1%. The more autonomously AI systems operate, the more important operational control becomes.
Source: Gartner, "2026 Hype Cycle for AI in IT Operations," July 2026.
97% of organizations that experienced an AI-related data security incident lacked adequate access control measures.
In many cases, therefore, the problem was not the AI itself, but rather the fact that no one regulated who or what could access the systems and the data.
Source: IBM, Cost of a Data Breach Report 2025.
In addition to current trends, you’ll also receive a specific set of criteria that you can apply directly to your own IT environment.

How can you find out which AI tools are already in use in your organization—and why do blanket bans often result in you seeing even fewer of them?

What data can leave the company, and what data cannot? And how can this be enforced technically, rather than relying solely on policies?

Entra ID app registrations, OAuth permissions, and the “Sign in with a Microsoft account” feature: What kind of access does a third-party AI app actually have—and how can you check this regularly?

Agent-based AI can perform operations autonomously in a production environment. What safeguards are needed: permissions, approval points, and rollback options?

What remains in the logs after an operation performed by AI—and what do you need to be able to trace in the event of an incident?

Who is responsible—the user, the in-house IT department, or the external service provider? Where are the boundaries, and what should be specified in the contract?
This webinar is intended for IT decision-makers at medium and large companies who, in addition to day-to-day operations, are also responsible for the development, automation, security, and future-readiness of their company’s IT systems.
Especially relevant if you:

CIO, CTO, IT manager, or responsible for IT operations;
is evaluating AI and automation options for the IT sector;
operates a complex infrastructure with a small in-house IT team;
wants to decide which processes are worth automating;
wants to clearly define permissions, approvals, and areas of responsibility;
wants to implement Copilot or other AI tools at the corporate level;
He wants to prepare the IT department for the challenges of the coming years as early as today.
01 | Shadow AI
Assessment methods, typical entry points—and why bans don't work on their own.
02 | DATA AND ACCESS
Data Classification in Practice, OAuth Authorizations, and Reviewing Application Registrations.
03 | AI IN THE MICROSOFT ENVIRONMENT
Copilot, agent-based workflows, permissions, SharePoint content, identities, and access to corporate data.
04 | WHEN AI ACTS ON ITS OWN
Permission restrictions, approval points, logging, and restoration—illustrated through a specific scenario.
05 | ACCOUNTABILITY AND SUPPORT MODEL
What should be handled in-house, what should be outsourced—and what needs to be specified in the contract?
Gloster has been developing, modernizing, and operating enterprise IT systems for more than two decades, while serving as the local enterprise partner for the world’s leading cloud, security, and AI companies. As a partner of Anthropic, we see agentic AI from the inside: we work with it every day in our clients’ systems, and we see where it can cause harm.
years of software engineering and enterprise IT experience
technology specialists across our international team
regions: Hungary, UK, Germany and the US
listed on the Budapest Stock Exchange
In addition to designing and operating enterprise Microsoft environments, we also work with leading vendor partners in the areas of cloud, networking, and security.
The starting point is corporate IT operations, not a specific technology. We’re examining how to keep everything under control while AI is already in use:
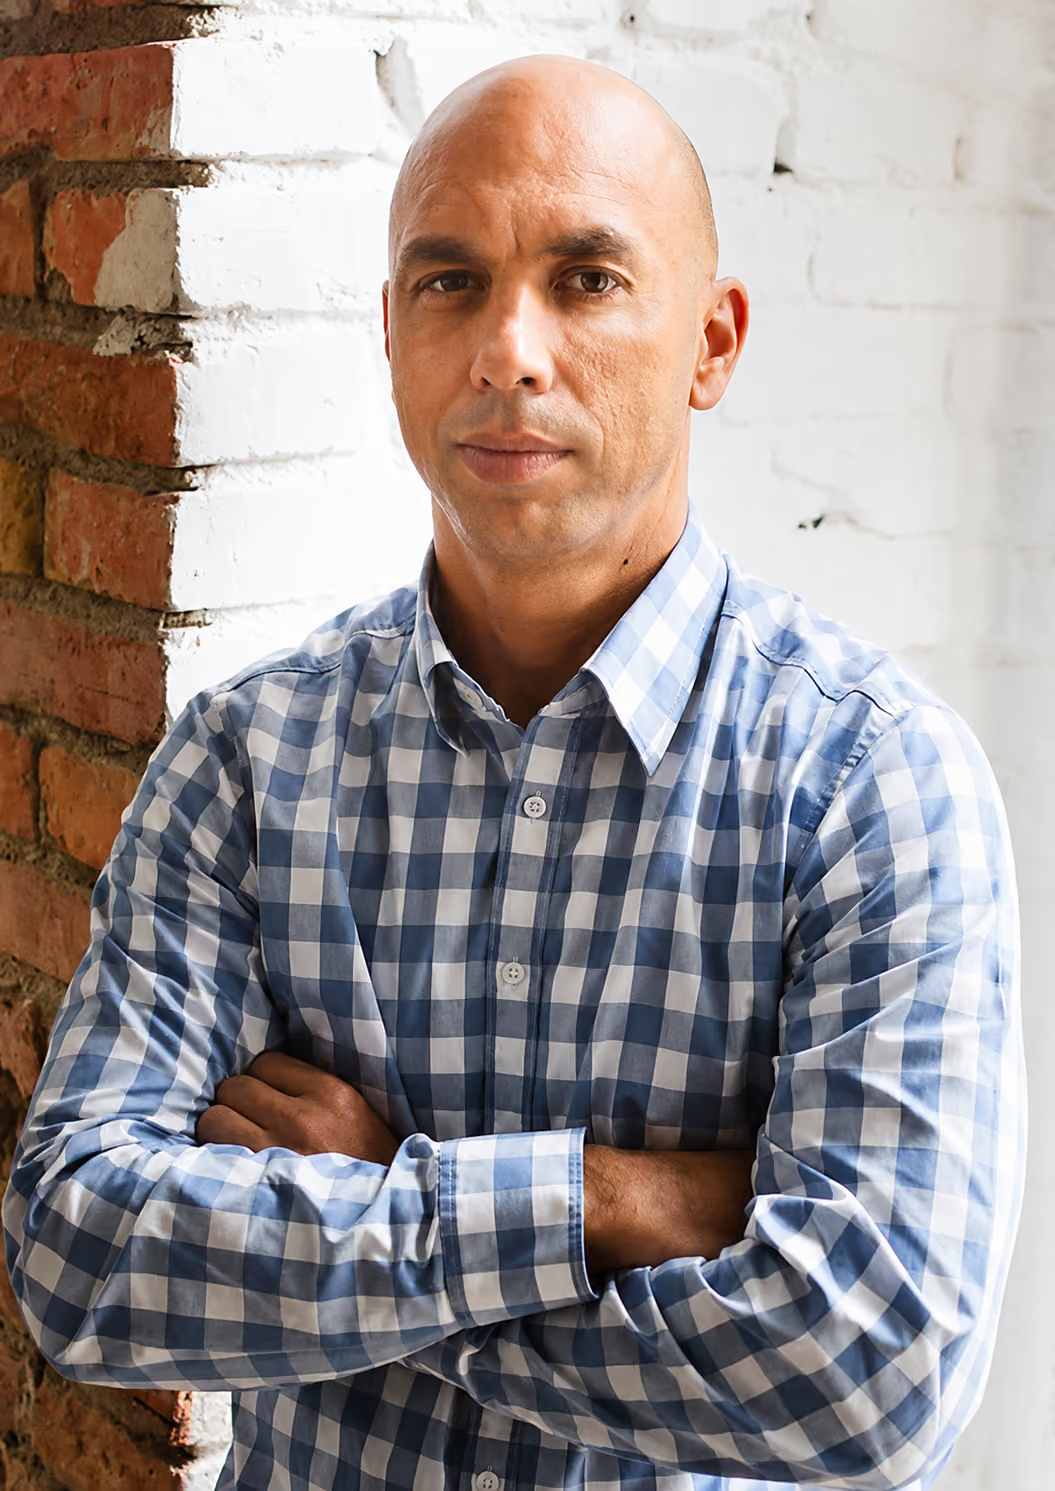
Attila Tóth leads Gloster Digital's operations in the DACH region and is responsible for enterprise-level programs and growth in German-speaking markets.
His work focuses on the needs of large corporations and the question of how new technologies can be integrated into existing IT environments in a secure and well-thought-out manner.
In this webinar, he will share insights from large-scale corporate projects in the DACH region: what issues are currently on companies’ minds regarding the use of AI, where new risks and responsibilities are emerging—and what IT decision-makers need to keep in mind during implementation and scaling.
Please fill out the form. We will confirm your registration via email within 48 hours and send you all the information you need to participate.